96%
Third-party plugins
7,633 vulnerabilities.
White Paper V3 · For decision-makers and compliance
"WordPress gets hacked all the time." Says who?
Of the 7,966 vulnerabilities found in the WordPress ecosystem in 2024, 96% were in third-party plugins and seven were in core itself. None of them with broad threat impact. This whitepaper delivers the source-backed figures, the hardening framework, and the fair comparison with custom code for your next security review.
/ 01 · Why this whitepaper exists
The security question rarely arrives with data. It arrives as a gut feeling, usually from IT or from someone in compliance, and it blocks the decision anyway. This whitepaper is the answer to it, in a form you can pass on internally.
The objection is understandable. But it confuses attack volume with code quality. Once you know the figures, the conversation moves to where it belongs: to operations.
Attack volume is confused with platform weakness. WordPress runs on around 41% of all websites and is therefore the single largest attack surface on the web. Attackers automate against the largest installed base. That is economics, not code quality.
Neglected plugins, delayed updates, weak passwords and cheap shared hosting. All of it is addressable, and none of it has anything to do with the choice of platform.
What a security officer wants to see is certificates, processes and figures with a source. That is exactly what the whitepaper delivers, so approval doesn’t stall on missing evidence.
/ 02 · Where the vulnerabilities sit
7,966 new vulnerabilities were found in the WordPress ecosystem in 2024. The distribution is the single most important data point for any sceptical reviewer.
7,633 vulnerabilities.
326 vulnerabilities.
Under 0.1%, none with broad impact.
In 2025 the core team found exactly two core vulnerabilities. The bad reputation comes from operations, not from the platform. For context: of the 7,966 vulnerabilities from 2024, Patchstack rated 69.6% as low priority. Raw counts overstate the real risk. Source: Patchstack, State of WordPress Security 2025, data from 2024.
of all websites worldwide run on WordPress, close to 59% market share among all CMS. More than all other systems combined.
W3Techs, July 2026of "basic web application attacks" use stolen credentials. The login is the vector, not the code.
Verizon DBIRof compromised CMS sites were running outdated software at the time of infection. Thanks to auto-updates, WordPress is outdated less often than other CMS.
Sucuri 2023password attacks were blocked by Wordfence in 2024 alone, plus over 1.1 billion SQL injection attempts.
Wordfence Annual Report 2024/ 03 · Your outcome
Not a plea for one platform. Six outcomes with which you close the security question on the facts.
Every value comes with its source and the year it was collected. In the meeting you are not holding an opinion, you are holding a data set.
Defense in depth from managed hosting to monitoring. Written so that a compliance lead can sign it off.
Both sides set out honestly, including the real advantages of hand-coded sites. That is exactly what makes the argument credible.
ISO 27001, SOC 2 Type II, data processing agreement, EU data centers and the two levels of GDPR compliance. Exactly the evidence that shortens vendor reviews.
Foundation before launch, access and resilience in week one, then ongoing governance. With clear thresholds for when a plugin gets replaced.
A dedicated section sets out which sources come from security vendors and where neutral sources such as Verizon, OWASP and W3Techs were used.
Free, in your inbox immediately, no sales call. All we need is a name and an email address.
/ 04 · The attack vectors
Knowing the vectors means you can close them deliberately. Almost all of them are addressable through operations and configuration, not through a change of platform.
Cross-site scripting
Broken access control
Cross-site request forgery
SQL injection and other injection
Remainder: auth, upload, disclosure
Distribution of the WordPress vulnerabilities disclosed in 2024 by type. Source: Patchstack 2025
That is the median time from a vulnerability being published to it first being exploited. 46% of the 2025 vulnerabilities had no vendor patch at all at the point of disclosure.
Which is why a firewall alone is not enough: in the 2026 pentests, generic WAFs caught only 12 to 26% of WordPress-specific exploits on average. WordPress-aware virtual patching belongs in the picture. Source: Patchstack 2026.
/ 05 · Defense in depth
A multi-layered hardening framework that a compliance lead can accept. The most important lever deliberately comes first.
Isolated containers instead of shared-hosting neighbours, Google Cloud infrastructure, two hardware firewalls, automatic daily backups and uptime monitoring every two to three minutes.
Auto-updates for core, themes and plugins, a minimal number of plugins, only maintained plugins, major updates on staging first.
WordPress-aware via Patchstack or Wordfence, plus Cloudflare DDoS protection. A generic firewall alone is demonstrably not enough.
Two-factor for every account with write access, strong passwords or passkeys, limited login attempts, no default "admin" user.
Automated daily, stored separately, with a tested restore. A backup without a proven way back is not a backup.
The lowest possible role per user, HTTPS enforced with HSTS, hardened configuration above the web root, security headers such as CSP and X-Frame-Options.
Server-side scanning, a vulnerability-intelligence subscription, high-priority gaps closed in hours rather than weeks.
/ 06 · Custom code compared
Honest rather than defensive. Hand-coded sites have real advantages. That does not automatically make them safer.
Security is determined far more by how a site is built, hosted and maintained than by whether it is WordPress or hand-coded. A well-maintained WordPress site on managed hosting is safer than a poorly maintained custom site with no patch process. And the other way round. The platform choice is subordinate to operational discipline.
/ 07 · Compliance and governance
Because the objection usually comes from someone in compliance, this part is decisive: WordPress can be run GDPR-compliant and to enterprise standards.
plus 27017 and 27018 for cloud and personal data
continuously monitored, not a point-in-time audit
EU data centers, data processing agreement in the dashboard
Encryption, access controls, EU data location and certifications. The host acts as processor; the data processing agreement under Art. 28 GDPR is part of it.
Consent banner, cookie and script blocking, privacy policy and a documented process for data subject rights. Plus serving Google Fonts locally, see Munich Regional Court, ref. 3 O 17493/20.
LILOX builds WordPress websites on managed hosting with exactly the hardening and compliance framework this whitepaper describes.
/ 08 · Recommendation
What has to be in place before launch, what follows in week one, and what runs permanently after that.
Managed hosting with verifiable certifications, EU data center, data processing agreement signed. Automatic core and security updates. Only reputable, maintained plugins, everything unused removed. HTTPS everywhere, wp-config hardened.
Two-factor for all admin and editor accounts, least-privilege roles, limited login attempts. Daily backups with a confirmed, tested restore. Activate WAF plus WordPress-aware virtual patching and DDoS protection.
Subscribe to vulnerability intelligence, patch high-priority gaps within hours. Server-side malware monitoring, quarterly plugin and user audits. Local Google Fonts, consent-controlled third-party scripts, data processing agreements kept current.
Thresholds
| Trigger | Consequence |
|---|---|
| A plugin with no update for twelve months, or with an unpatched high-severity gap | Replace immediately or apply virtual patching |
| Processing of special categories of personal data or payment data | PCI-DSS controls, hourly backups, extended monitoring |
| Maintenance discipline cannot be guaranteed in-house | Prefer managed hosting and a maintenance retainer. Operational discipline decides, not the platform |
/ 09 · What’s inside
Built for people who have to defend the result internally. 11 pages, five figures, and a disclosed source base.
The core message in three sentences, written for the meeting.
The distribution of vulnerabilities across plugins, themes and core, plus the actual causes of compromises.
Which gaps get exploited in practice, and how quickly after disclosure.
Seven layers of defense plus the concrete steps on updates, authentication and configuration.
Certificates, the two levels of GDPR compliance, and what a security officer wants to see.
Both sides set out honestly, with the bottom line on operational discipline.
Before launch, first week, ongoing operations. With three threshold rules.
Context on the data, the disclosed interests of the vendor sources, and the full source selection.
/ 10 · Is this for you?
Written for decision-makers as well as security, IT and compliance leads who have to justify or approve a platform decision.
/ 11 · Who stands behind it
If your IT team or your external security officer has follow-up questions on the whitepaper, we answer them directly.
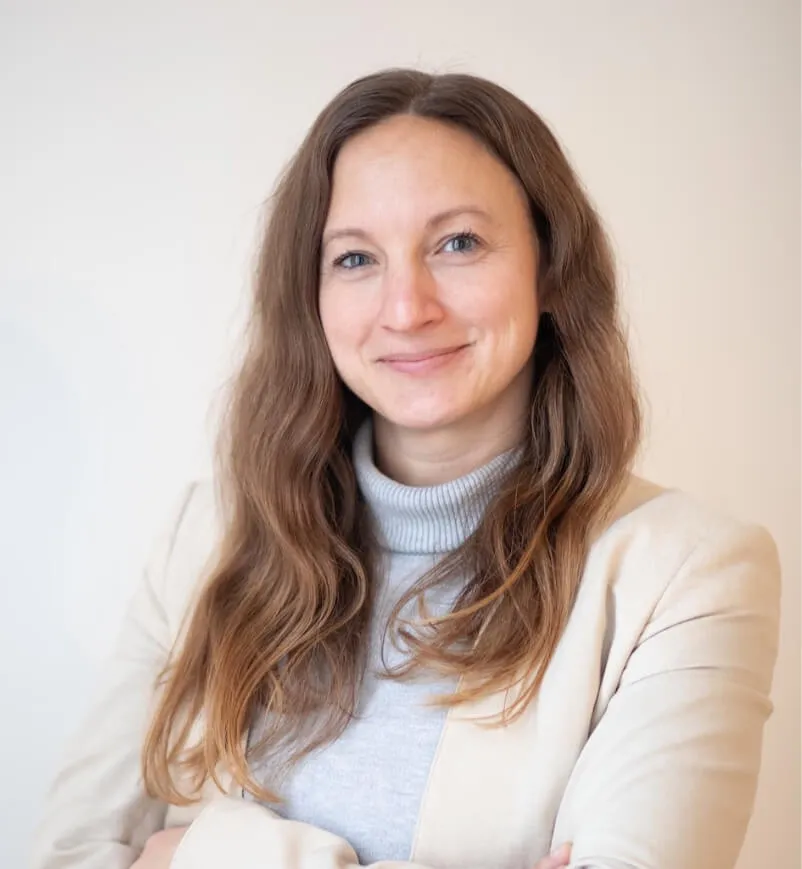
15 years in digital marketing, around ten of them exclusively in B2B. She has sat on both sides: as the client who had to justify agency budgets, and as the executive expected to deliver pipeline at the end of the quarter.
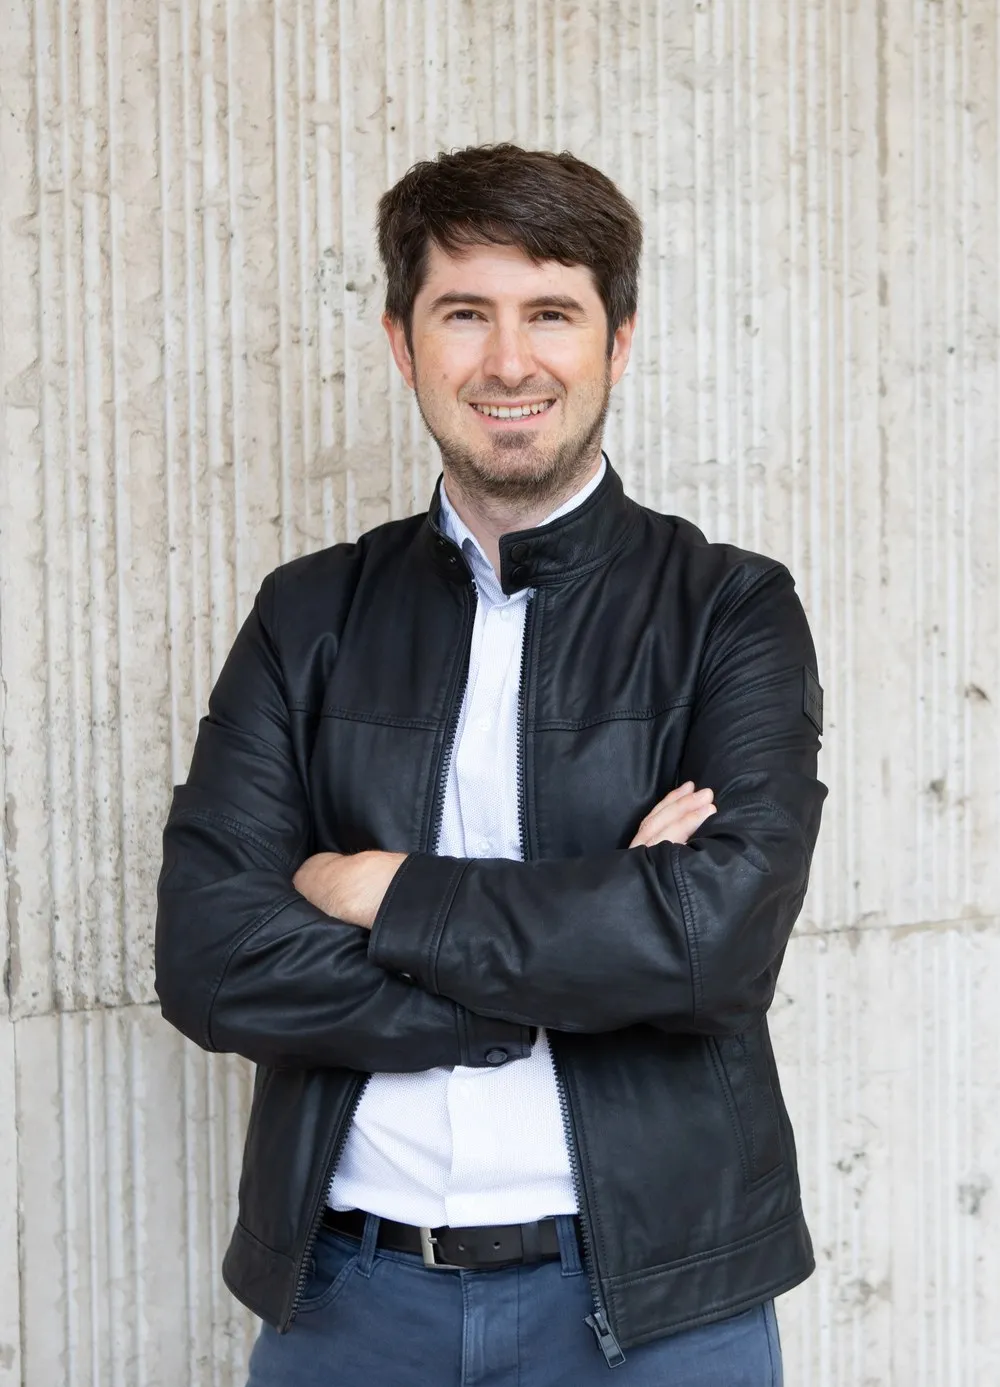
Mechanical and industrial engineer with an international MBA. 15 years in industry as project lead for large-scale projects, Head of Engineering and plant manager. He knows acceptance processes in which evidence counts and assurances do not.
Competent, friendly, committed, and doesn’t just tell you what you want to hear. Advice between equals, no fluff, always focused.
 Prof. (FH) Dr. Uwe HeilDr. Heil KG Consulting & Coaching
/ 12 · Frequently asked questions
Run professionally, yes. Of 7,966 vulnerabilities from 2024, 96% were in plugins, 4% in themes and seven in core. What matters is managed hosting, update discipline, two-factor authentication and monitoring.
WordPress runs on around 41% of all websites and is therefore the single largest attack surface on the web. Attackers automate against the largest installed base. Sucuri itself makes clear that the high WordPress share of cleaned infections reflects popularity and says nothing about platform security.
Not automatically. Custom code has a smaller attack surface and no public exploit database, but it is usually unreviewed, without community review, without automatic security patches, and it carries key-person risk.
Yes, on two levels. The infrastructure needs encryption, access controls, EU data location and a data processing agreement. The application needs consent management, script blocking, a privacy policy and a process for data subject rights.
No. In the 2026 pentests, generic firewalls caught 12 to 26% of WordPress-specific exploits on average. Because the median time to first exploit is five hours, WordPress-aware virtual patching belongs in the picture.
The whitepaper is free. Processing under GDPR, servers in the EU, no sharing with third parties. No phone call without your invitation. You can unsubscribe from the newsletter at any time with one click.
Download
11 pages, in German, with five figures and a sources section you can pass straight to your IT team.
11 pages in German, five figures, one sources section to pass on.
The data sources cited come predominantly from security vendors that make money protecting WordPress. The whitepaper sets out that interest in a dedicated section and additionally draws on neutral sources: Verizon DBIR, OWASP and W3Techs. The Sucuri figures are from 2023, the main Patchstack data set from 2024. References such as whitehouse.gov or NASA are publicly documented WordPress installations and not LILOX clients. The whitepaper is not legal advice.
/ 13 · Next step
We work through the seven layers of defense on your existing website and you get the result in writing, in a form you can put straight into the review.
A cookie for LILO?
With your consent, LILO answers your question right away in the chat, and we can see which content actually helps. Without it, LILO stays off. Everything else on this site works exactly as before.
LILO runs on Intercom. With your consent, the chat window is loaded, Intercom sets its own cookies, and chat messages are processed there. The workspace is located in the USA. The chat opens right after you consent.
Your choice applies to this website and can be changed at any time via “Cookie settings” in the footer.